
Decide whether the device meets the FD&C Act 524B definition of a cyber device and write down the reasoning. Then write the Cybersecurity Management Plan: who owns security work, how exploitability and severity are rated, which threat modeling method is used, which scanning tools run during development, how updates reach the field and how vulnerabilities are monitored after release. Pick the penetration testing approach at the same time so scope, vendor and lead time fit the schedule.
On the map: Cyber device call (FD&C 524B). Cybersecurity Management Plan. Choose the pen-test approach.
Rows are disciplines, columns are stages 1 to 8. Select a square to open that task.
Back to the full map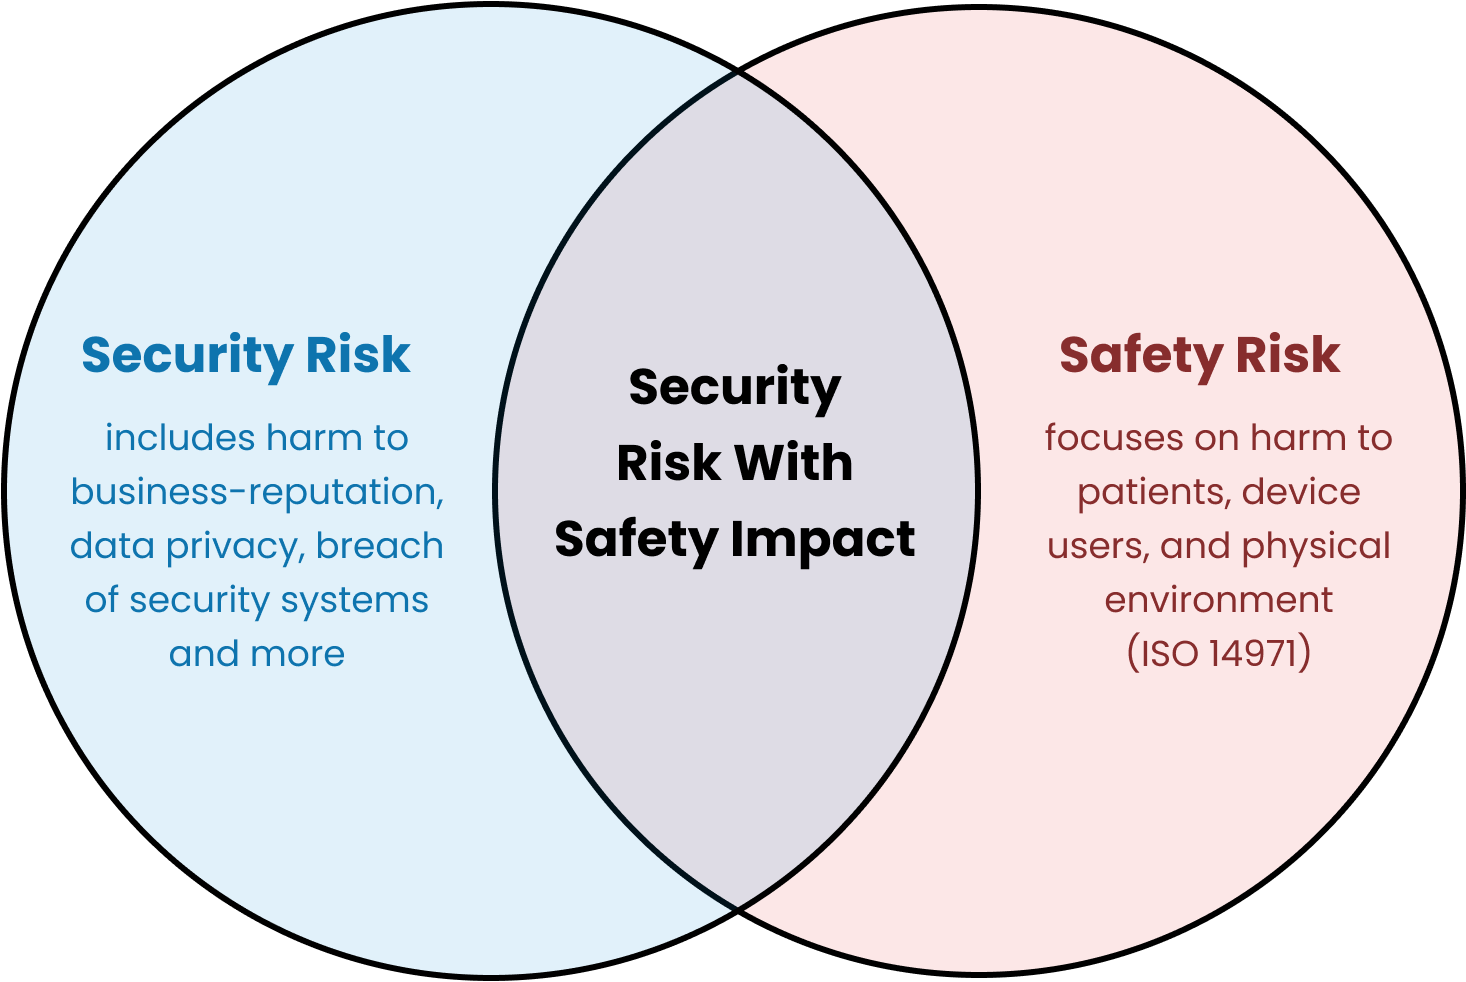
Make the cyber device call with engineering's real connectivity list and regulatory's reading of 524B. A wrong call here is the most expensive late surprise in this lane.
Read the three statutory criteria against the real deployment. Software that runs on an internet-capable host, accepts network or removable-media input, or receives updates usually qualifies. An offline container still counts when its host can reach a network. The safe default is to plan as a cyber device and keep each artifact proportionate to the actual attack surface.
FDA now expects a separate, parallel and interconnected security risk process. The plan defines an exploitability scale in place of probability, its own acceptability matrix, and a trace from any security risk with patient-harm potential into the ISO 14971 file.
Scope from the attack surface: network ports, file parsers, update path, service access. A very small surface can support a narrow test. The tester must be independent of the developers and qualified, so in most projects this means an outside firm. Book the vendor early because lead time and a retest window land right before submission.
Name the tools and gates up front: static analysis and dependency or container scanning in CI, SBOM generated as a build artifact, code review, two-factor access to the repository, and a patch timeline. Naming them in the plan makes the later evidence routine output from the pipeline.
See the open positions and apply.