
After clearance the SBOM of each released version is scanned for new vulnerabilities and each one is assessed for exploitability and patient impact. Controlled risks are fixed in routine updates. Uncontrolled risks follow FDA's 30-day customer notification and 60-day fix timeline. A coordinated disclosure policy lets outside researchers and customers report vulnerabilities and get an acknowledgment.
On the map: Monitor SBOM vulnerabilities. Patch within the 30/60-day windows. Coordinated disclosure.
Rows are disciplines, columns are stages 1 to 8. Select a square to open that task.
Back to the full map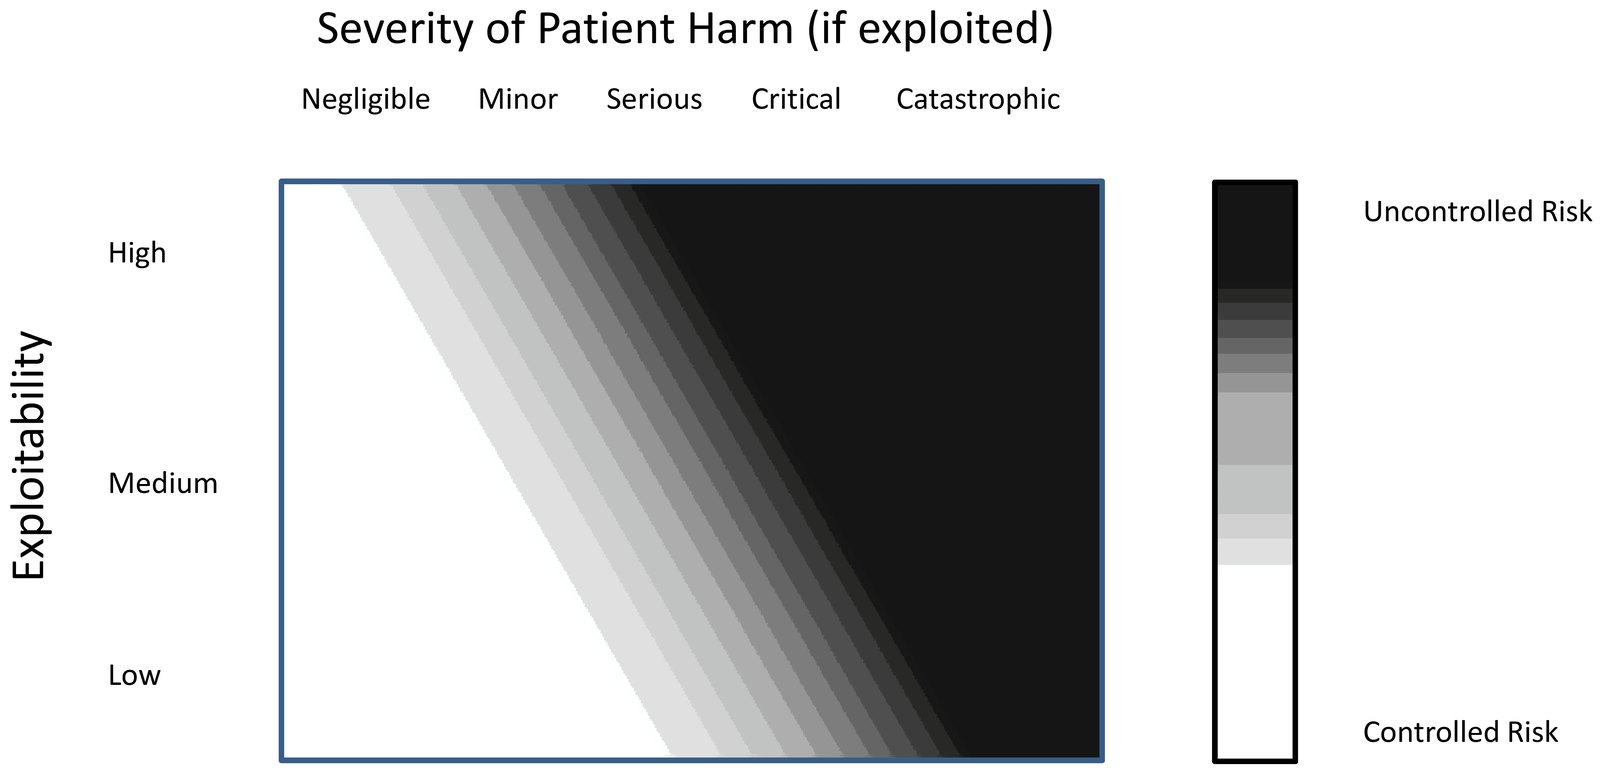
Run SBOM vulnerability monitoring alongside engineering's release cadence and quality's complaint and CAPA process, so a disclosed vulnerability has an owner, a patch path and a regulatory assessment.
A scanning tool watches the SBOM for every version in the field. Each hit is checked for applicability to the device, then rated on exploitability and severity of patient harm. FDA asks for a binary call on each one: controlled or uncontrolled.
Controlled risks go into routine updates on a regular cycle, as section 524B expects. These are device enhancements that need no 806 report. For an uncontrolled risk with no known adverse events, customers are notified with interim compensating controls within 30 days, and a validated fix is distributed within 60 days. ISAO membership is the other condition under which FDA does not enforce 806 reporting.
A published intake channel and a coordinated vulnerability disclosure policy, based on ISO/IEC 29147 and 30111, set who receives reports, how receipt is acknowledged and how findings reach risk management and CAPA. Section 524B requires a plan that includes coordinated disclosure.
Most security patches are enhancements and are handled under change control with a letter to file. If the fix changes the architecture, interfaces or intended performance, the change is assessed for a new 510(k). The SBOM and threat model are updated with each release.
See the open positions and apply.